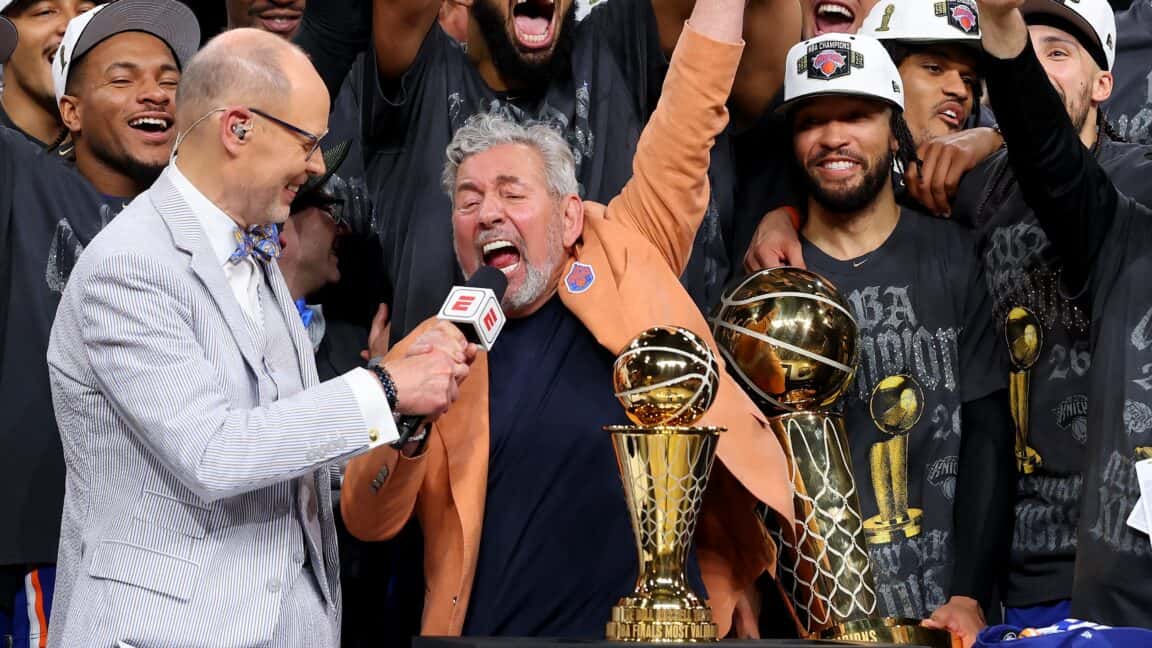
Corporate phishing tests are common, but this one was especially cruel.
To respect copyright, we link to the source rather than republishing the full text. Read the complete article on Ars Technica.
 Skip to content